

Cybersecurity Governance
Governance, Risk & Compliance Services for Confident Decisions
We help organisations set clear security governance, understand risk, and meet compliance requirements with a practical programme that supports the business instead of slowing it down.
- Security Governance Frameworks
- Risk Assessment & Management
- Compliance Readiness
- Policy & Control Design
- ISO 27001 Certified Practices
Our Technology Partners
Built on Trusted Technology Platforms
We work across leading cloud, CRM, and AI platforms, so every recommendation is based on what fits your business, not a single vendor.

Why GRC
Why Businesses Need Governance, Risk and Compliance
As regulations grow and threats change, security decisions need clear ownership, consistent controls, and evidence that they work.
Unclear Security Ownership
Without defined roles, security decisions are delayed or made inconsistently.
Unmanaged Risk
Risks are not identified, ranked, or tracked, so effort goes to the wrong places.
Growing Regulatory Pressure
New standards and customer requirements add to compliance workload.
Scattered Policies
Outdated or inconsistent policies leave gaps that auditors and attackers find.
Manual Evidence Gathering
Audits become stressful when evidence is spread across teams and tools.
Third-Party Exposure
Vendors and partners introduce risks that are not always assessed.
Our Services
Our Governance, Risk & Compliance Services
We help you build a GRC programme that fits your size, industry, and risk profile.
Security Governance Framework
Define roles, responsibilities, decision rights, and reporting for security.
Risk Assessment
Identify, analyse, and prioritise risks to systems, data, and operations.
Risk Management Programme
Set up processes to treat, track, and review risks over time.
Compliance Readiness
Prepare for standards and frameworks such as ISO 27001, SOC 2, GDPR, and HIPAA.
Policy & Procedure Development
Write and update practical security policies that teams can follow.
Control Design & Testing
Design security controls and check that they work as intended.
Third-Party Risk Management
Assess and monitor the security of vendors and partners.
Audit Support
Organise evidence and guide teams through internal and external audits.
The GRC Pillars
The Three Pillars of an Effective GRC Programme
Governance, risk, and compliance work best when they are planned together rather than as separate activities.

Governance
Clear ownership, policies, and decision-making for security across the business.

Risk
A consistent way to identify, prioritise, and manage risks that matter.

Compliance
Controls and evidence that show you meet regulatory and customer requirements.
Our Process
Our GRC Consulting Process
We build GRC programmes step by step, starting with what matters most to your business.
Understand
Learn your business, regulatory obligations, systems, and current controls.
Assess
Identify gaps in governance, risk management, and compliance.
Prioritise
Rank actions by risk, effort, and business impact.
Design
Define frameworks, policies, controls, and responsibilities.
Implement
Put processes and controls in place with your teams.
Monitor
Review risks, controls, and compliance status on a regular cycle.
Industries
GRC Services Across Industries
Each industry faces its own regulations and risk priorities.
Financial Services
Governance and controls for regulated financial data and systems.
Healthcare
Compliance support for patient privacy and clinical systems.
SaaS & Technology
Security assurance that supports customer trust and enterprise sales.
Retail & eCommerce
Controls for payment data and customer information.
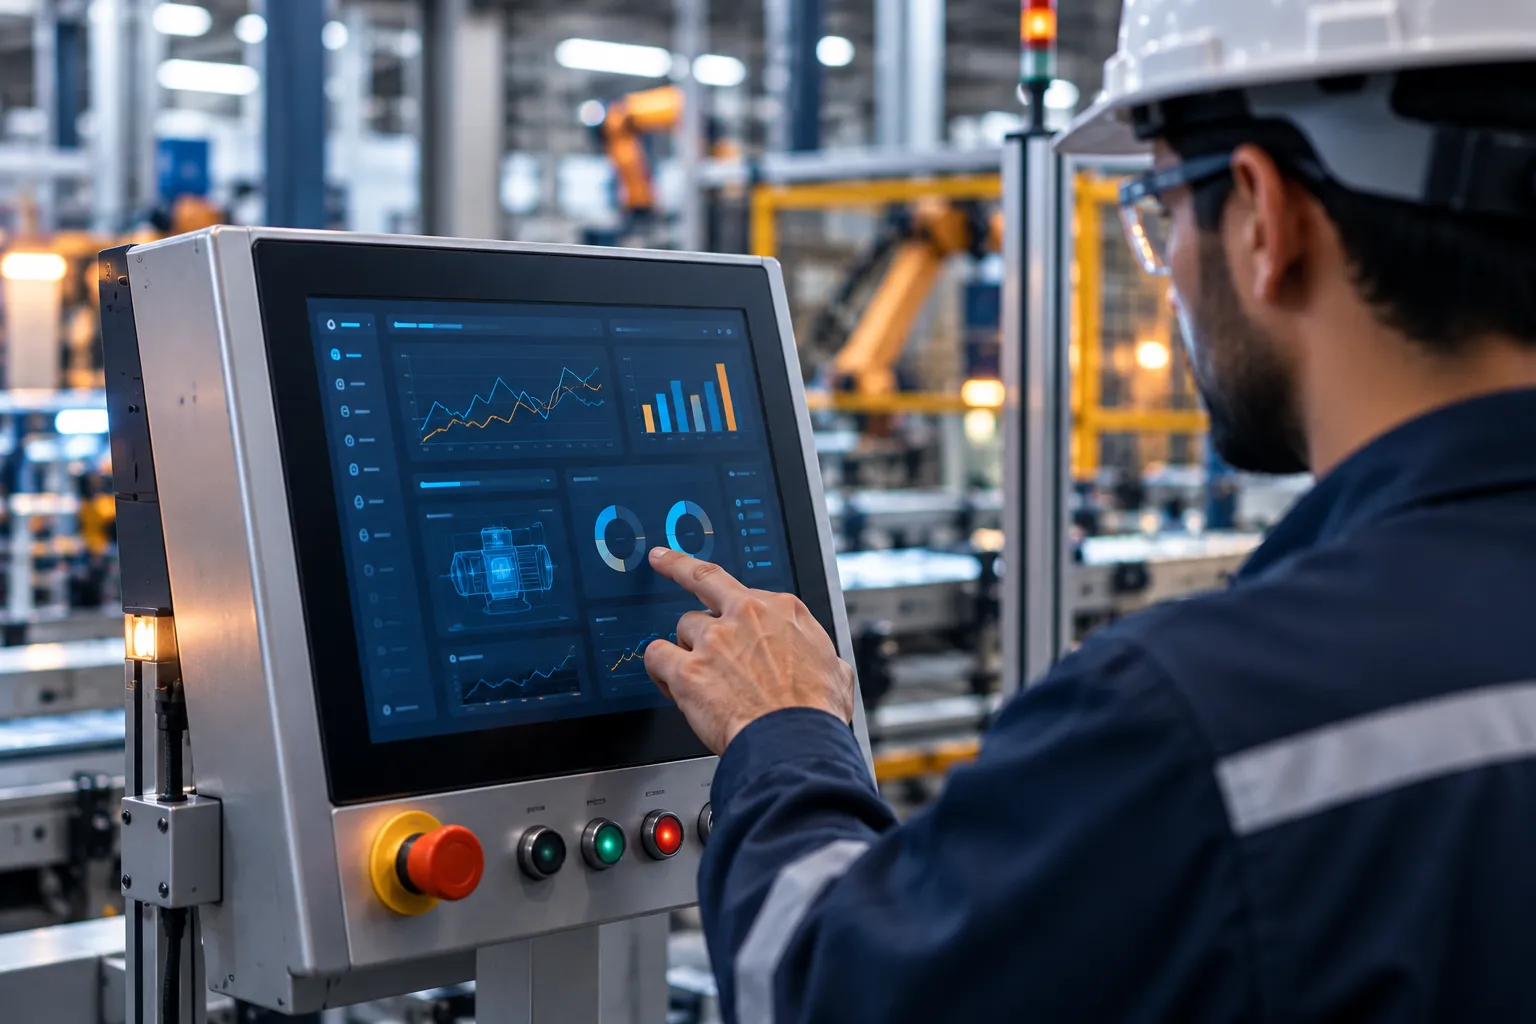
Manufacturing
Risk management for connected operational systems.
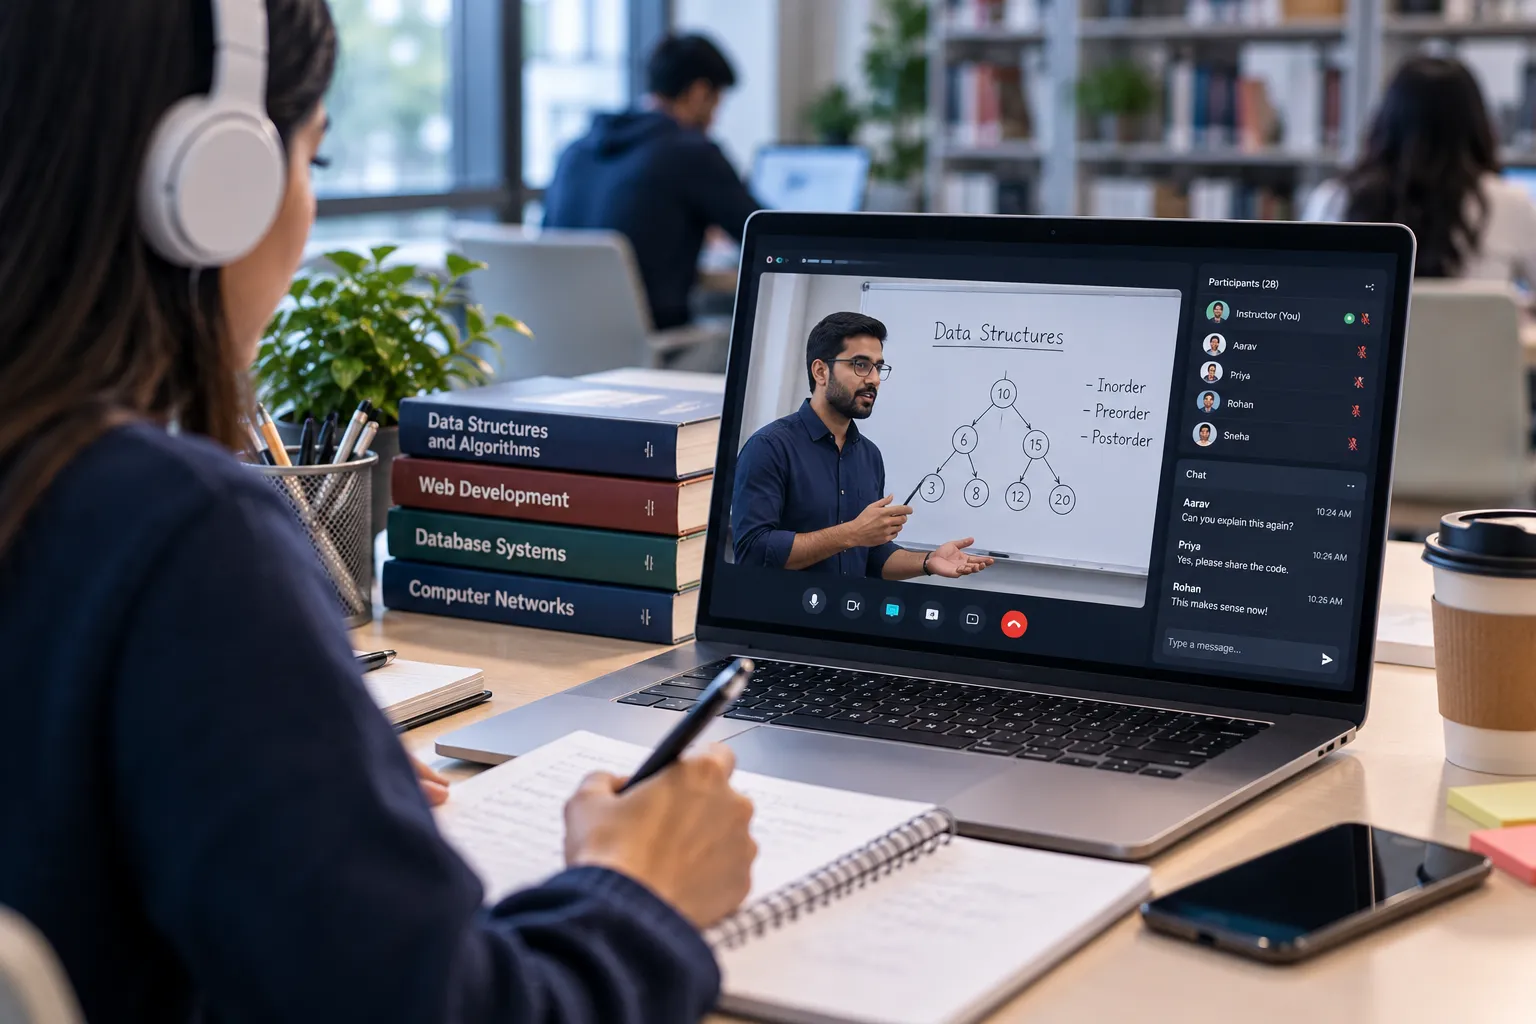
Education
Governance for student data and learning platforms.
Why Wildnet Edge
Why Choose Wildnet Edge for GRC Services
We combine security expertise with our own experience running ISO 9001, ISO 27001, and ISO 42001 certified practices.
Practical Frameworks
Programmes sized to your organisation, not copied from a template.
Certified Practices
We follow the same standards we help clients prepare for.
Business-Aligned Risk
Risk decisions linked to business priorities, not just technical findings.

Clear Documentation
Policies and procedures written so teams can actually use them.

Audit Readiness
Evidence organised and ready before auditors ask for it.

Ongoing Support
Regular reviews to keep governance and compliance current.
Engagement Models
Flexible GRC Engagement Models
Choose the support that matches your compliance goals and internal capacity.
GRC Assessment
A gap analysis with a prioritised improvement plan.
Compliance Programme
End-to-end preparation for a specific standard or framework.
Virtual Compliance Team
Ongoing GRC expertise without a full in-house team.
Audit Support
Focused help preparing for and managing audits.
In Their Words
Rated 4.89 across 104 reviews
Quotes are from engineering and product leaders, the people who own the outcome.
“Partnering with Wildnet Edge was a game-changer for our department. Their deep understanding of government processes, combined with cutting-edge AI capabilities, helped us modernize outdated systems with minimal disruption. The result? A faster, smarter, and more transparent public service delivery model.”
“Wildnet Edge truly exceeded our expectations. Their AI-first approach helped us streamline product development and automate key workflows, allowing our team to focus on innovation. Their proactive collaboration and agile execution felt like having a tech co-founder on our side.”
“Working with Wildnet Edge was transformative. They brought deep expertise in AI, cloud, and agile delivery that enabled us to modernize legacy systems without disruption. Their ability to deliver complex solutions at scale made them an essential partner in our digital evolution.”
Straight answers
The questions you were going to ask on the call.
Clear expectations make better partnerships. Here is where the conversation starts.
What does governance, risk and compliance mean?
GRC is a combined approach to setting security ownership and policies, managing risk, and meeting regulatory and customer requirements.
Which compliance frameworks do you support?
We support preparation for frameworks including ISO 27001, SOC 2, GDPR, and HIPAA, depending on your industry and markets.
How long does compliance readiness take?
It depends on your current controls and the framework. A gap assessment gives a realistic timeline before work begins.
Do we need a full-time compliance team?
Not always. Many organisations use a virtual compliance team to cover GRC needs cost-effectively.
Can you help with vendor risk?
Yes. We assess and monitor third-party vendors and partners as part of your risk programme.
Do you support us during audits?
Yes. We help organise evidence, prepare teams, and respond to auditor questions.
Contact Us
Let’s Build for Outcome
Let’s co-create solutions that deliver measurable impact.
Get started
The Technology Edge Your Business Deserves.
A working session, not a pitch. 30 minutes session on solving your problem.
Prefer to just pick a time? Book a 30-minute roadmap call